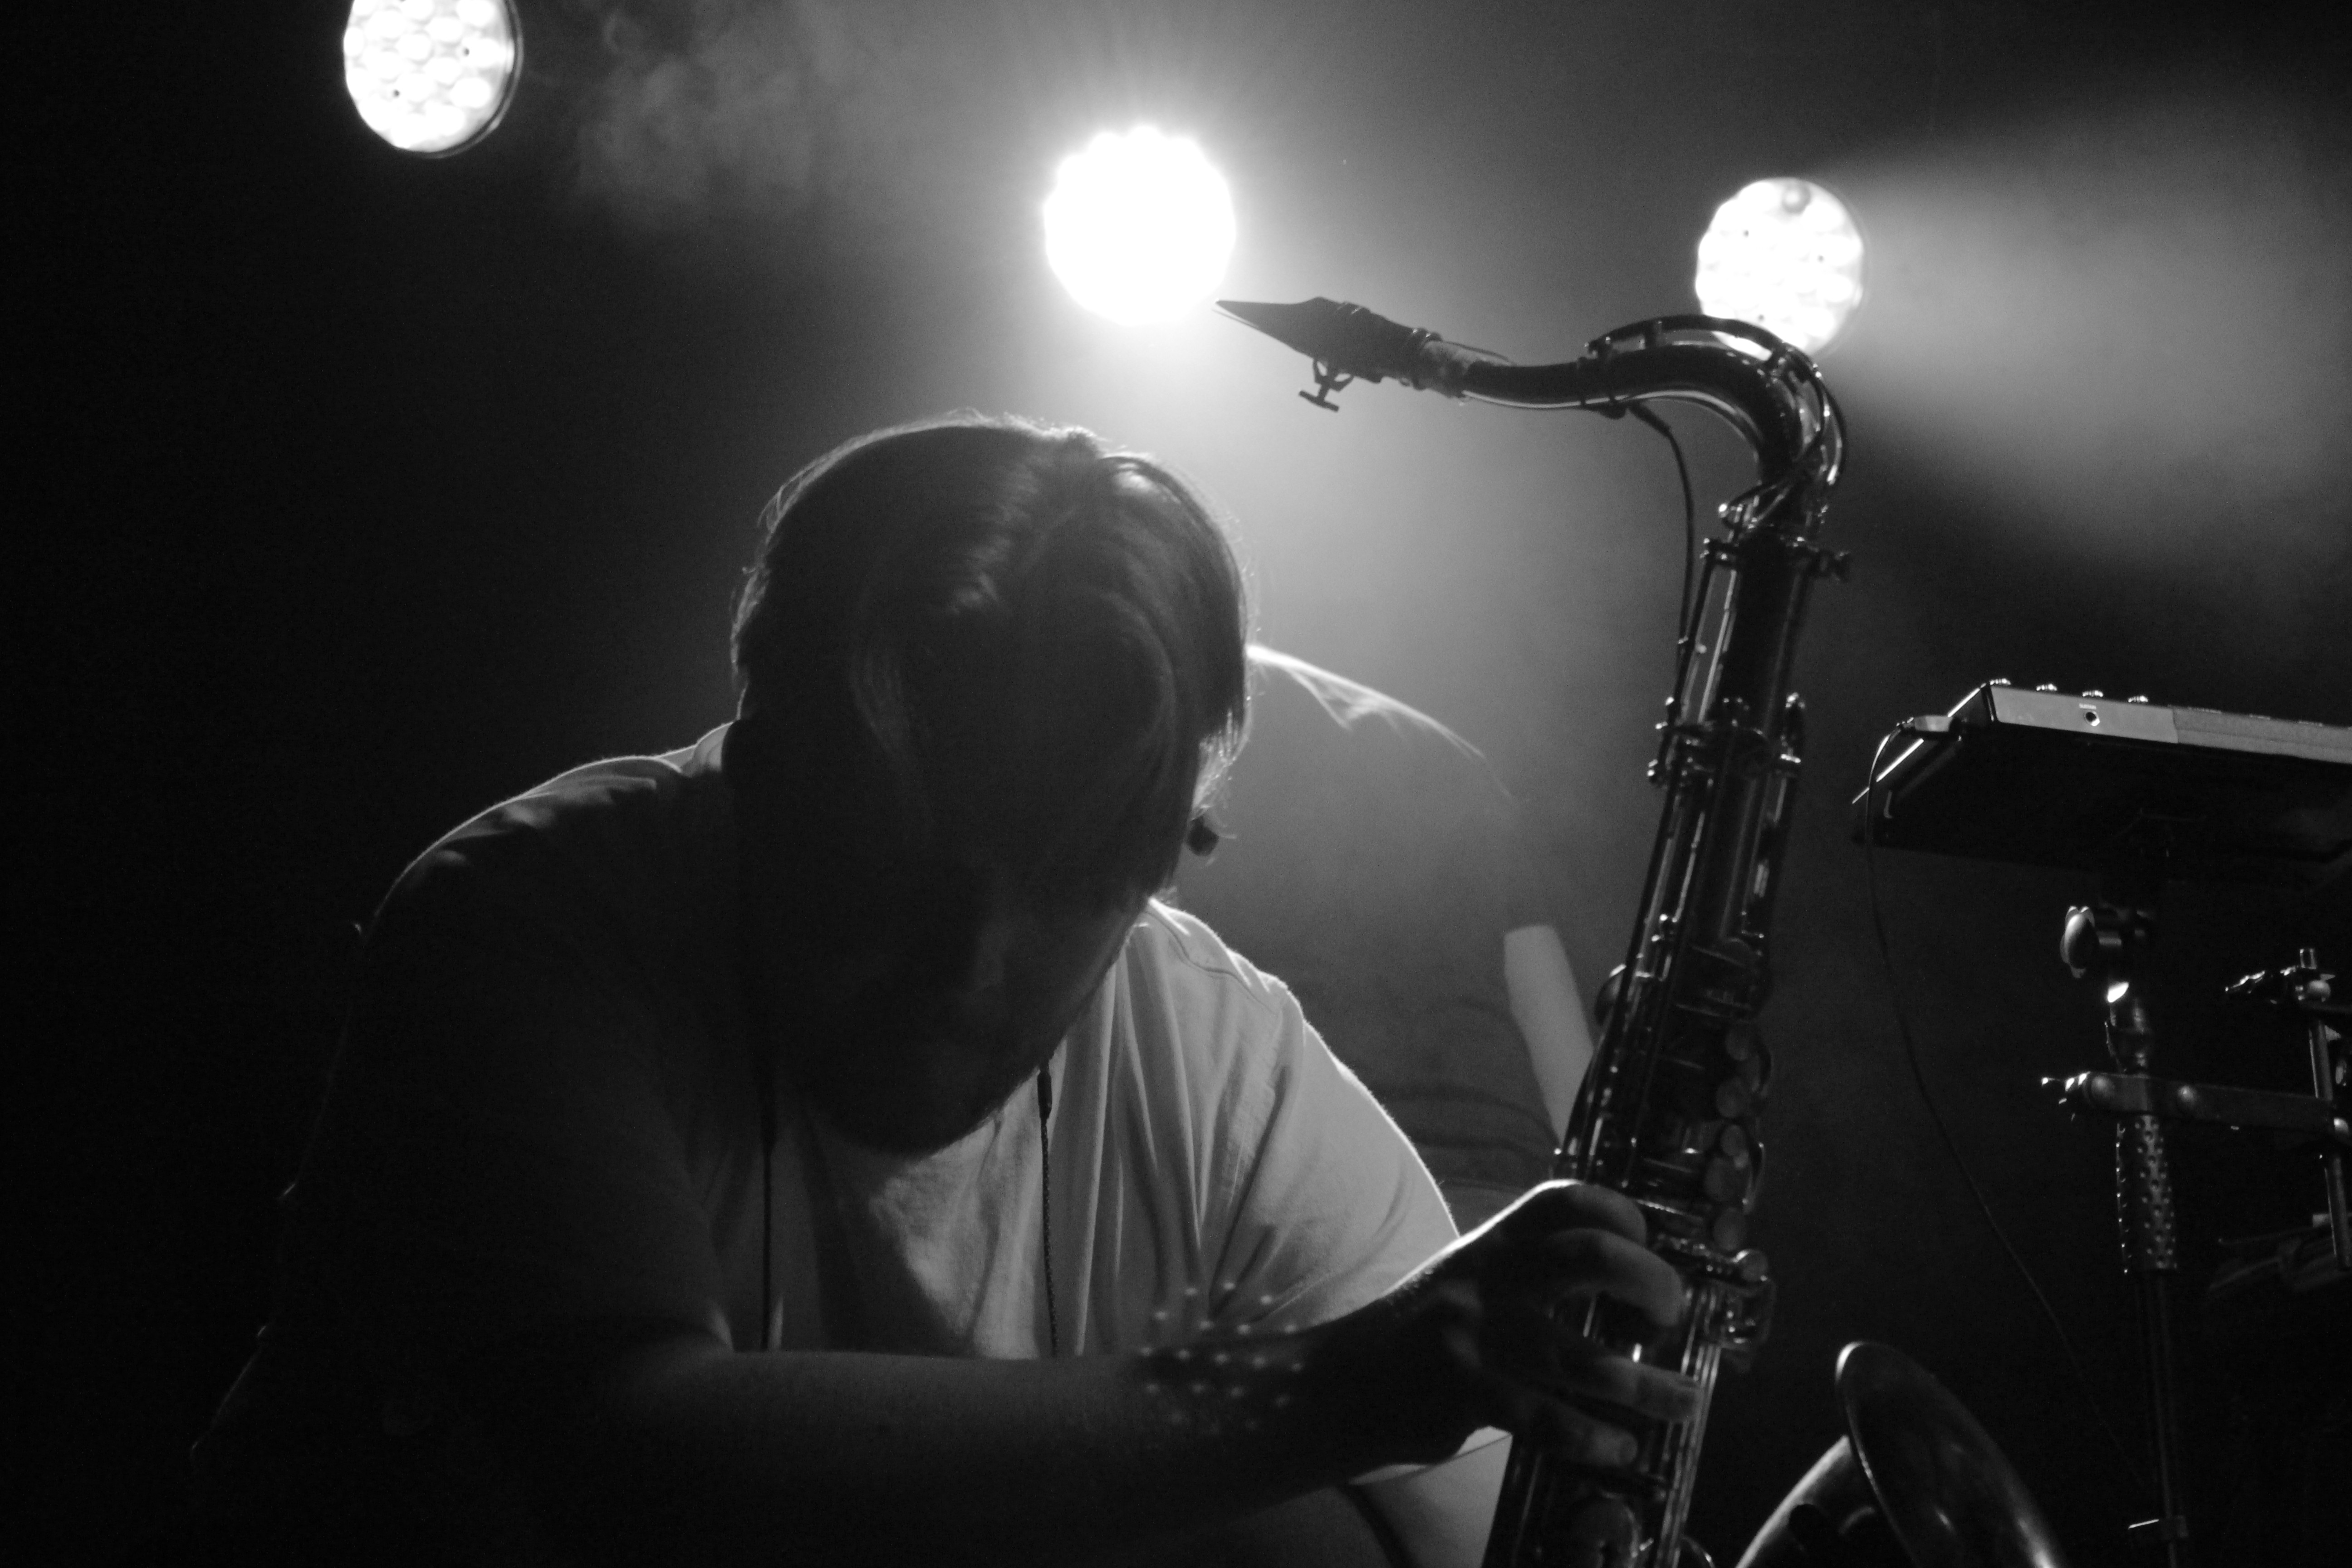
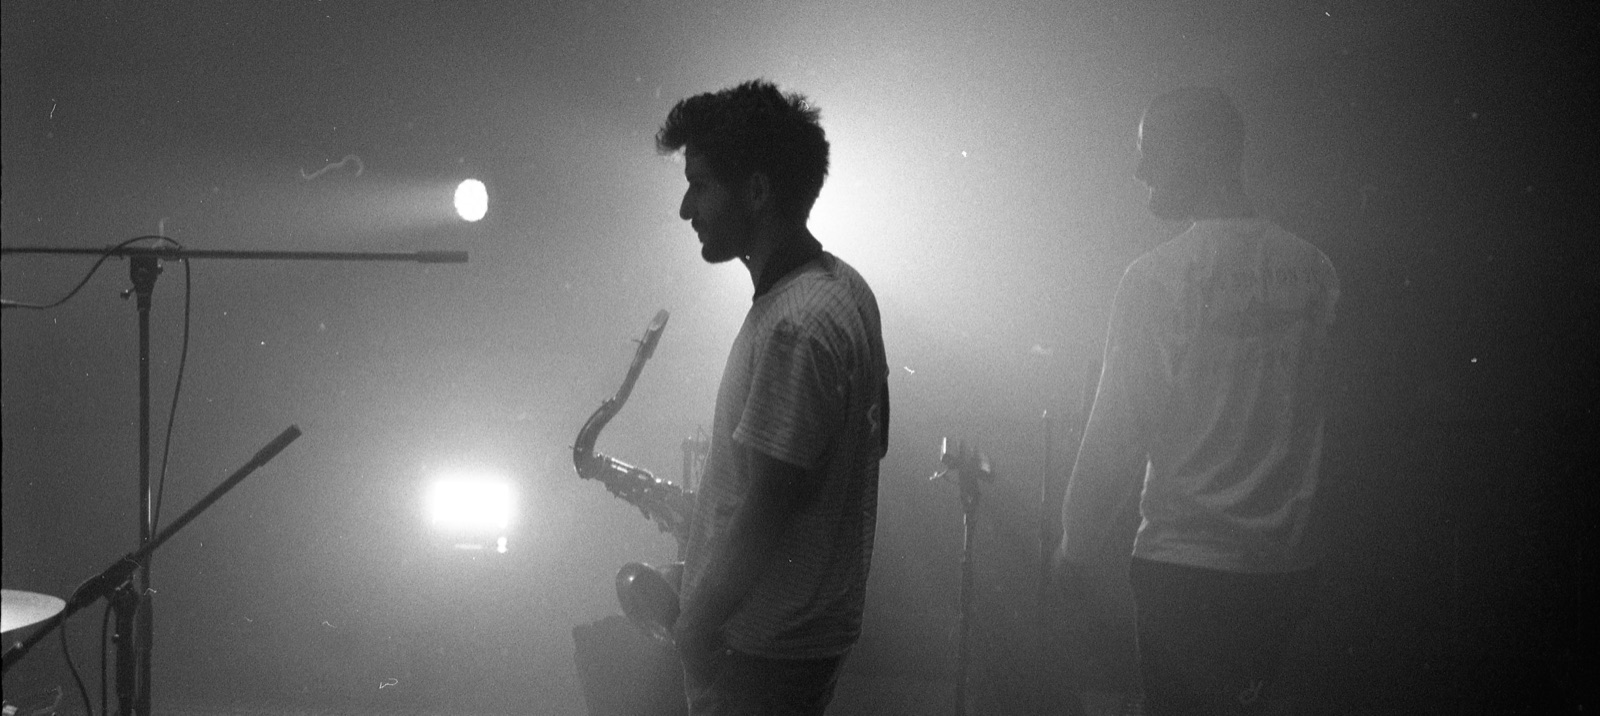
Thibault Barillon on stage with a saxophone, backlit through haze
thib.space

Thibault Barillon

I'm Thibault, a trained engineer turned Product Manager with expertise in cybersecurity, as well as a creative most notable for my saxophone work as part of Robocobra Quartet, but I also tinker with acrylic, living art, and code art.

photo · Colin Armstrong

From saxophones to petri dishes and code art

2026 Live

Live from the Sonic Lab

Writing · saxophones · film edited by me
Sonic Lab, SARC · Belfast
2024 Photography

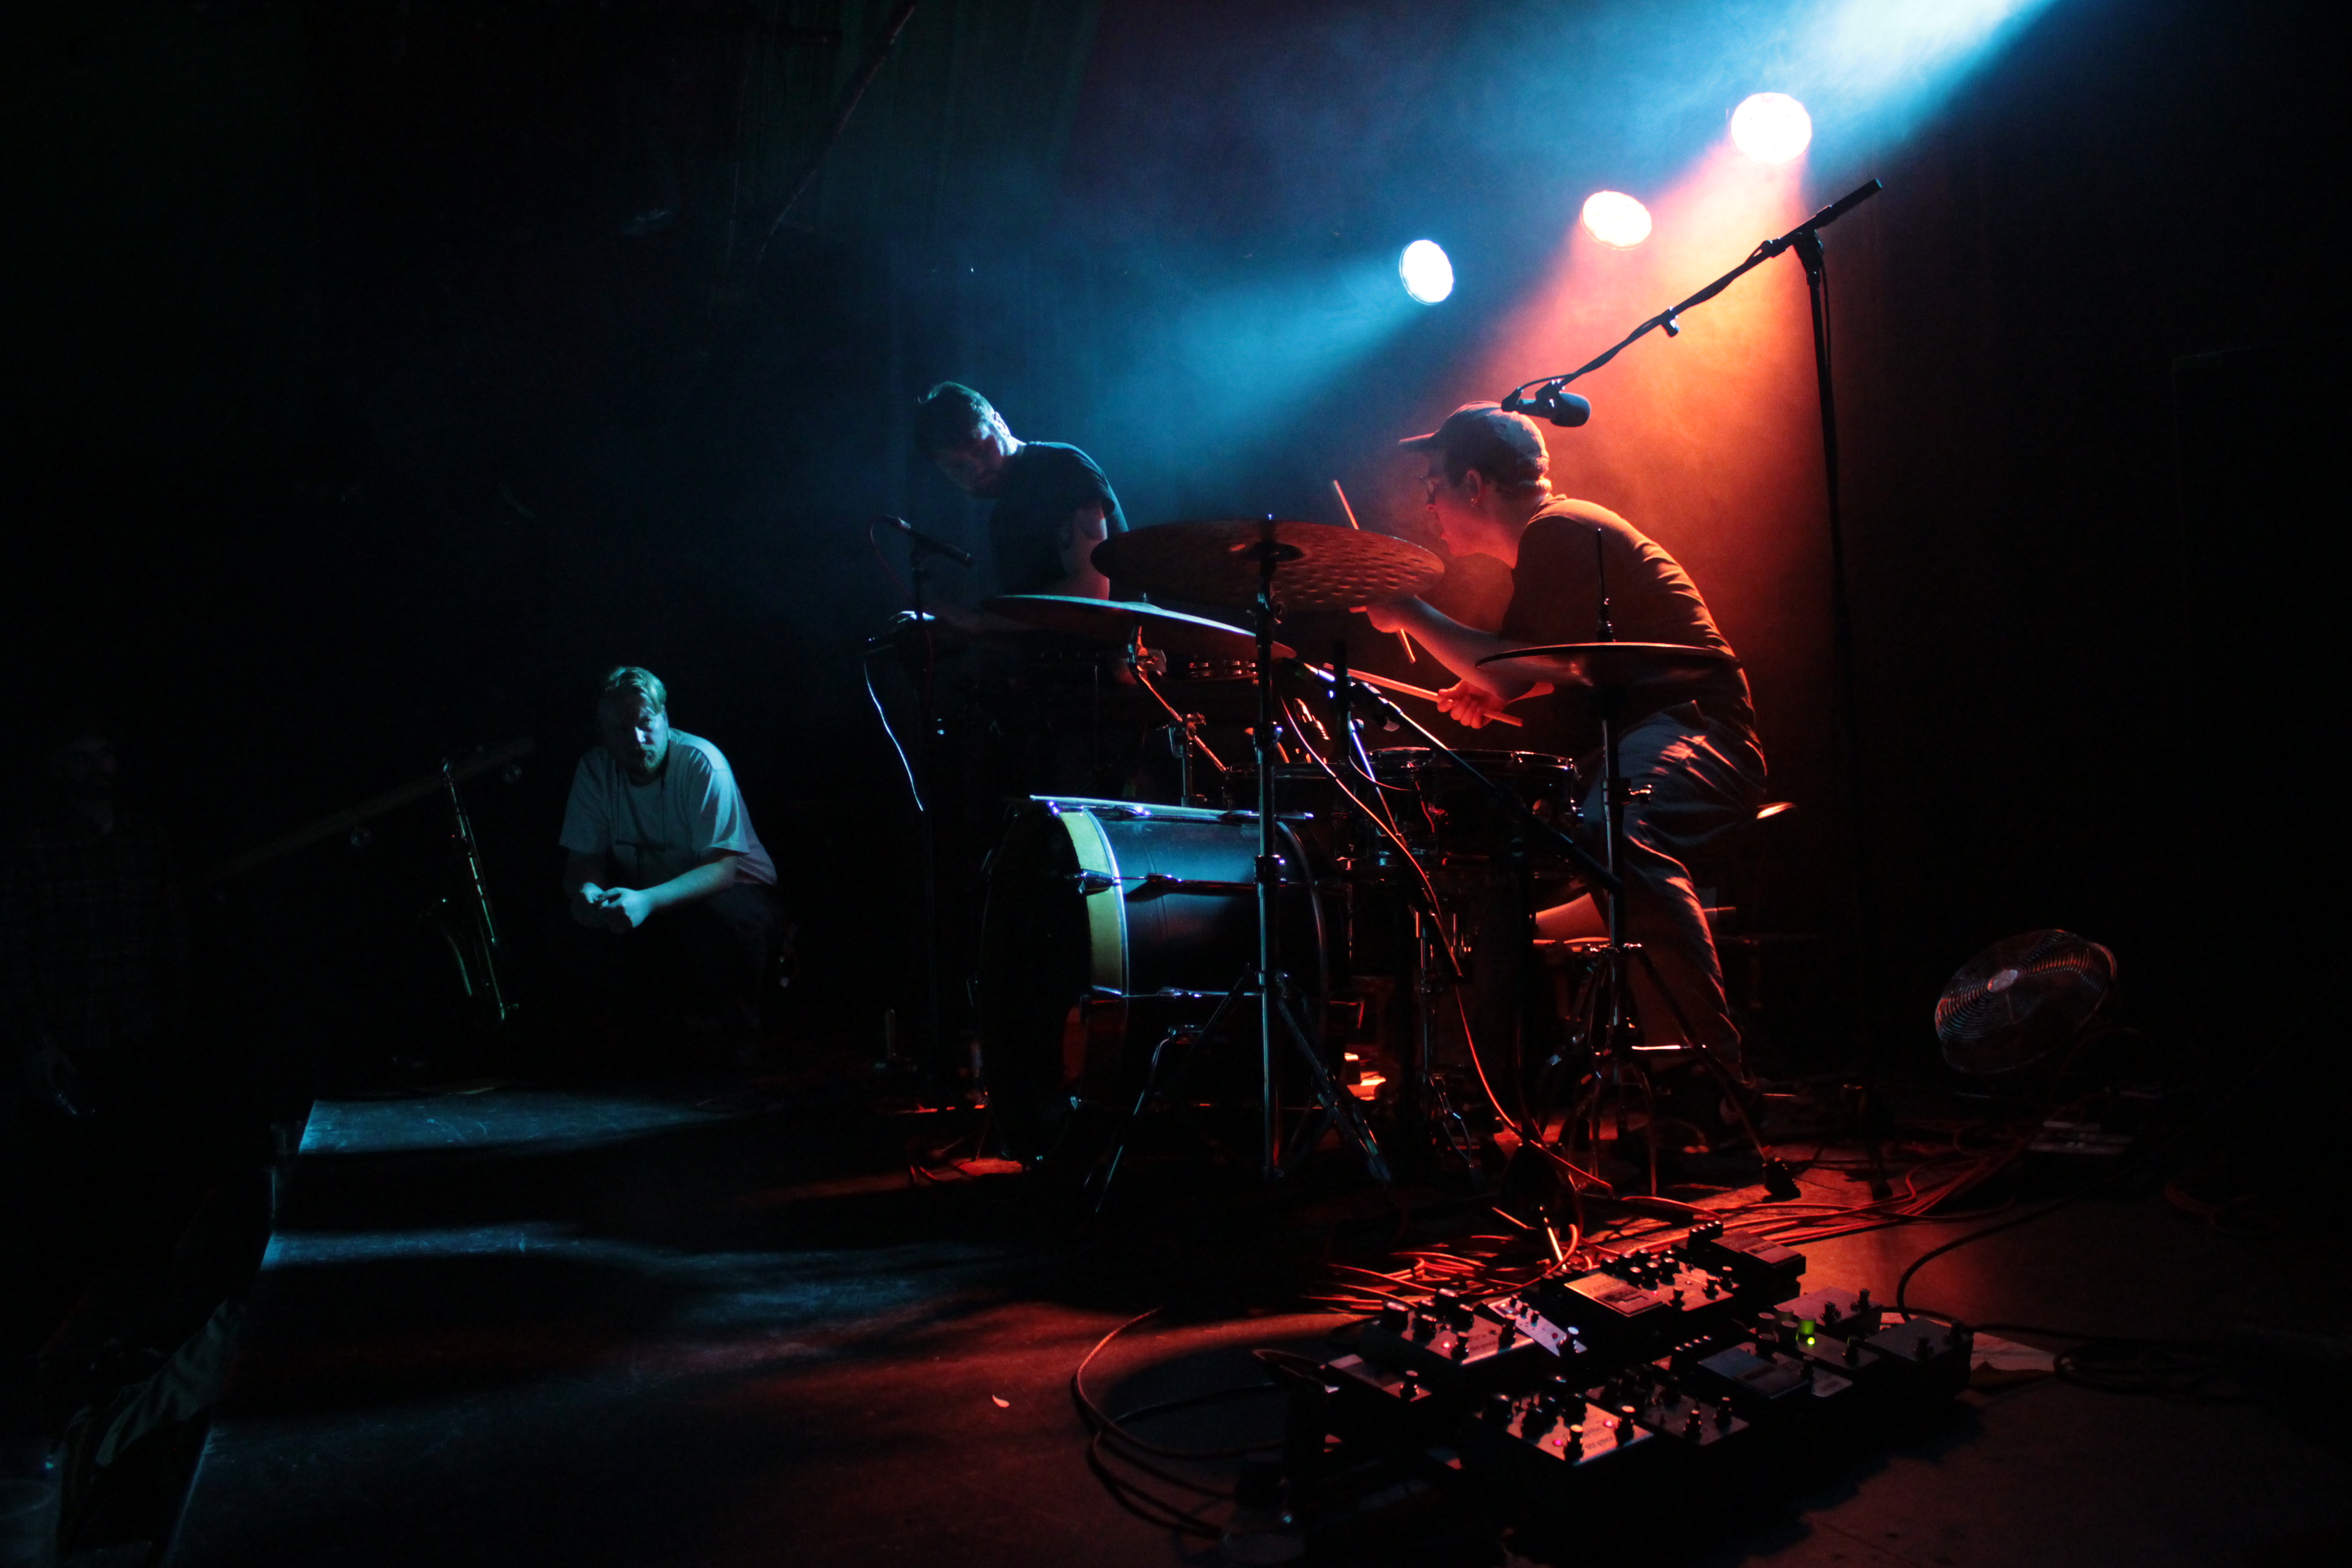
Live photo — Robocobra Quartet — Grand Social, Dublin — 24 Feb 2024

2023 Visual

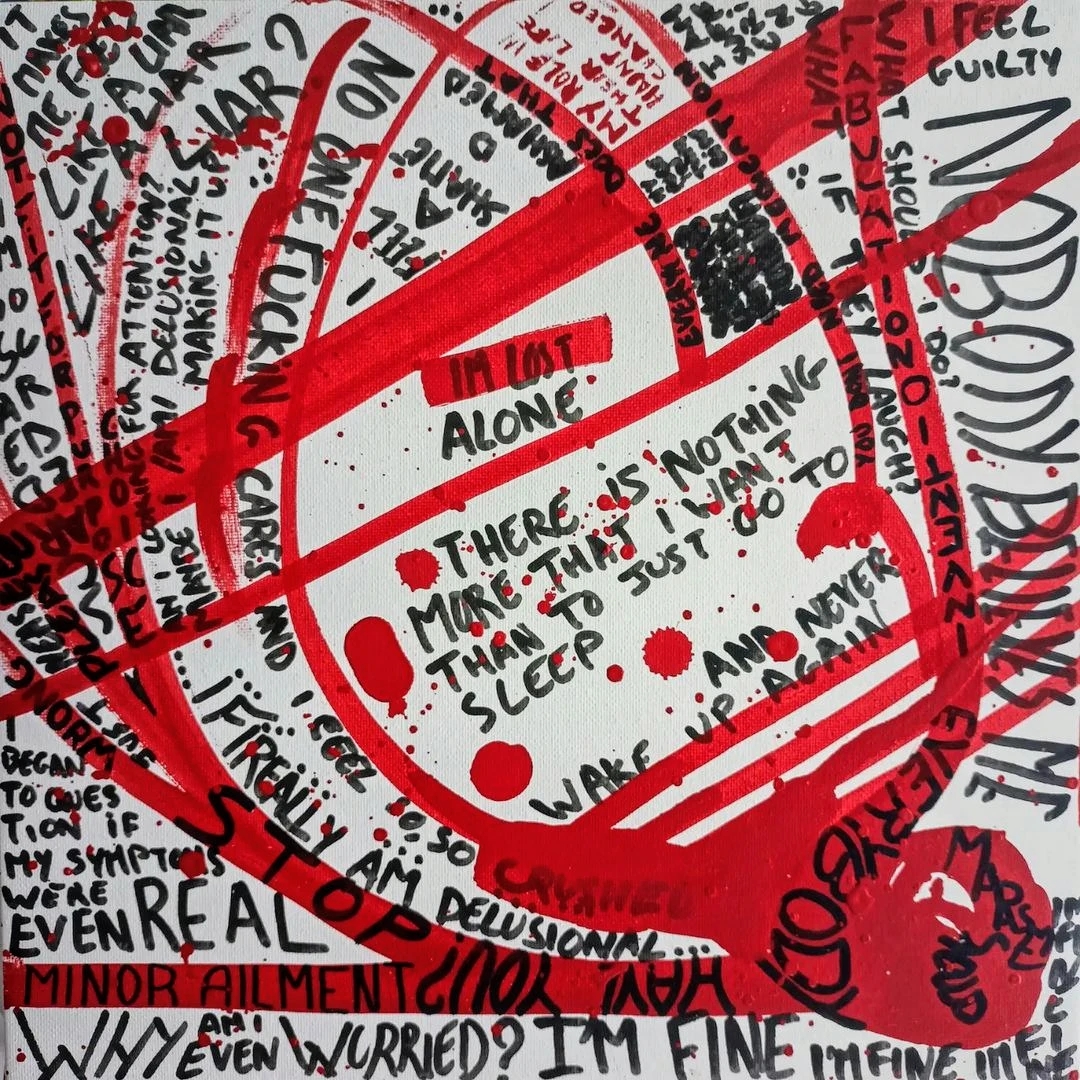
Acrylic Marker on Canvas

17 June 2022 LP

Living Isn't Easy

Writing · saxophones · Robocobra Quartet

"A storied triumph"

★★★★ · MOJO

"Thank god for Robocobra Quartet"

★★★★ · The Irish Times

"Belfast jazz agitators hit career-best"

★★★★ · The Line of Best Fit
2022 Award

NI Music Prize — Album of the Year

◆ Northern Ireland Music Prize · 2022

Awarded to Living Isn't Easy.

2022 Live

Live at Glastonbury

Writing · saxophones · Robocobra Quartet
Glastonbury · full set
2021 Live tape

Live Tape 1

Writing · saxophones · Robocobra Quartet
2019 Live

Bar 37 Will Shock You!

Writing · saxophones · Robocobra Quartet
Sonic Lab, SARC · Belfast
2019 Live

You'll Wade — live on the BBC

Writing · saxophones · Robocobra Quartet
BBC session
18 November 2016 LP

Music for All Occasions

Writing · saxophones · Robocobra Quartet
2015 EPs

Iwazaru Mizaru & Bomber EP

Writing · saxophones · Robocobra Quartet
Iwazaru Mizaru · 2015
Bomber EP · 2015
2015 Live

Live at The Black Box

Writing · saxophones · Robocobra Quartet
The Black Box · Belfast
1990
Born · Nantes, France
Art›

Fifteen years building security products — the short version.

2025 — now Current
Principal Product Manager · Contrast Security

Runtime application security — ADR, which catches attacks inside live applications. I own the integrations portfolio: getting that attack evidence into the SIEM, SOC and AI tools security teams already use. In the first year I shipped eight SIEM integrations and a universal event forwarder I'd proposed; more recently, the developer experience for the next-generation platform's public APIs. (Senior PM 2025, Principal since 2026.)

2023 – 2024
Senior Product Manager, SaaS Program · IBM Security

Product lead for IBM Security's SaaS transformation across the SIEM and XDR portfolio.

2021 – 2023
Senior Product Manager · IBM Security

Strategy and lifecycle for the threat-detection portfolio. Drove consolidation onto a single cloud-native platform, and a QRadar SIEM turnaround that lifted commitments on customer feature requests from 77% to 99%.

Wrote:
What is XDR?2021

Originally published on securityintelligence.com, 12 October 2021.

Extended detection and response (XDR) is a security solution that delivers end-to-end visibility, detection, investigation and response across multiple security layers. Core components of an XDR architecture include federation of security signals, higher-level behavioral and cross-correlated analytics, and closed-loop and highly automated responses. This creates a truly unified experience supported by a solutions architecture that equals more than the sum of its parts. Security teams are able to get more value from an XDR that meets the following criteria:

  • Supports open standards
  • Delivers advanced analytics
  • Provides a simpler, unified analyst experience
  • Streamlines operations
  • Enhances response through automation

An XDR solution can achieve improved visibility across an organization's networks, endpoints, SIEM and more via open-system integration. Open standards can help move the industry away from expensive and wasteful 'rip and replace' programs. Instead, an open approach helps organizations get more out of their existing investments.

An XDR solution can also offer more automation and AI enrichments at all levels of detection, analytics, investigation and response. Automation throughout the threat life cycle can dramatically reduce mean time to detect (MTTD) and mean time to recovery (MTTR). Not only does reducing these metrics have a direct relationship to mitigating the cost of a data breach, it also frees up time for analysts to do more human-led activities like investigation. An XDR solution also bolsters investigation with a unified view of threat activity, a single search and investigation experience and consistent enrichment with threat intelligence and domain expertise.

Is XDR just another acronym or a fundamental market shift?

For many decades now, emerging threats have put organizations at risk. As the IT landscape evolved and threat actors found new ways to attack, security teams needed to find new ways to detect and respond to threats.

Today, this evolving theme of complexity continues. And the list of point solutions being deployed to overcome these burgeoning threats goes on and on — from SIEM, to cloud workload protection, to endpoint detection and response (EDR), to network detection and response (NDR) and more. While these investments each do their part to solve immediate and dire issues, in combination they've created a bigger challenge: how to use and get value from them together.

This is why we call them point tools; they were made to address specific challenges. Now that security teams face a myriad of challenges, it's never been more critical to have them work in concert. Without doing so, limited security operations resources will continue to be spread thin, total cost of ownership will continue to increase, and pinpointing and responding to threats will continue to be time-consuming and inefficient.

Extended detection and response is the beginning of a shift towards uniting multiple siloed solutions and reducing the complexity that impedes fast detection and response. Gartner identified XDR as the number-one security and risk trend at the end of 2020, suggesting now is the moment when all this complexity — too many tools, too many alerts, too little time — is coming to a head, with XDR as a response.

What are the different approaches to XDR?

Industry analysts have outlined two approaches: native and hybrid. Native XDR is a suite that integrates with a vendor's own solutions to collect telemetry and execute response actions. Hybrid or open XDR is a platform that integrates with various vendors and third parties to do the same.

Vendors have been taking different approaches to what is under the hood of XDR. Does XDR = EDR plus additional capabilities? Or EDR plus NDR, or some other combination? It may be too soon to tell where the market lands as the technology is nascent, but the delineation between native and hybrid XDR is one thing the industry seems to agree on.

How does XDR 'extend' SIEM?

For some readers, SIEM may have immediately come to mind. There are key differences. In XDR, correlation and alerting tend to be fully automated, employing use cases provided and tuned by the vendor, and incident response focuses on highly repeatable actions that can be automated — sending a suspicious file to a sandbox, enriching an alert with threat intelligence, blocking an email sender tied to phishing. This differs from SOAR, which can be broadly customized with playbooks and used to unite people as well as technology.

XDR can extend the detection and response capabilities enabled today by SIEM. In fact, SIEM can play an integral role in an XDR architecture, gathering, organizing and assessing massive amounts of data for SOC analysts; XDR builds on the data and events flowing through it. When you receive analytics from a SIEM, endpoints and networks separately, it can be like having three different witnesses to an attack — XDR brings all three together into one complete story.

How does XDR compare to MDR?

Even as XDR vendors strive to untangle the complexity problem, it will take time. Compounding the challenge is the skills shortage: the need for talent to run analysis and investigations leads many organizations to use a partner for managed detection and response (MDR) services.

MDR is an approach to managing sophisticated detection and response tools — via endpoint, network or SIEM technology — often with proactive threat hunting and 24/7 SOC coverage. As one analyst put it, "XDR success still seems to be based on human expertise," making MDR an invaluable companion to XDR for customers who could use a helping hand.

How does XDR support customers with zero-trust aspirations?

Zero trust is a framework that starts with an assumption of compromise, then continuously validates the conditions for connection between users, data and resources to determine authorization and need. XDR provides an essential function to zero trust by continuously monitoring for incidents and responding in the most targeted way possible to avoid disruption to the business.

Instead of placing blind trust in a system and saying the controls are enough, with XDR you constantly monitor the places where things could go wrong — which is exactly why identity tools such as identity and access management (IAM) play a critical role tying into XDR architectures.

What should customers look for in an XDR solution?

Your XDR should be an open, extensible solution that lets your organization get more from its existing investments. Look for third-party integrations that spare you a costly rip-and-replace, and cloud-native solutions for cloud visibility. XDR goes far beyond an improved EDR; it should be the end game for threat detection and response, as part of a unified platform.

Ultimately, XDR makes it easier for the people managing and responding to threats every day to do the work. Advanced analytics, constantly updated threat intelligence and a streamlined experience free analysts to spend their time on investigations, not gathering data. People and culture are the keys to the SOC, and by uniting threat-detection data and tools, XDR enables the collaboration and openness that helps teams thrive.

Offering Manager, Threat Detection & Response — IBM Security
2018 – 2021
Product Manager · IBM Security

Roadmap for QRadar SIEM and Vulnerability Manager. Ran the withdrawal of QRadar's vulnerability-assessment capability — ~600 customers migrated to Tenable and Qualys with zero escalations — and kicked off an OT / industrial-IoT security strategy.

Wrote:
How Growing Businesses Should Tackle Cybersecurity Challenges2020

Originally published on securityintelligence.com, 1 July 2020.

When we think about the most public cyber attacks and data breaches, we generally associate them with large enterprises. The truth is cyber attacks are not limited by company size. A significant cyber attack can happen to any company, in any industry and of any size.

According to the 2019 Cost of a Data Breach report by the Ponemon Institute, "small businesses face disproportionately larger costs relative to larger organizations when it comes to breaches."

Typically, one of the most valuable assets for any sized company is its data, and data theft or destruction is probably the most frequent result of cyber attacks on small and medium businesses (SMB). SMBs can be very profitable targets for bad actors, because they have fewer resources and little in-house expertise to plan, implement and execute a cybersecurity incident response plan. Business drivers and modernization needs make it an even trickier balancing act with the norm of working from home.

So how can SMBs protect themselves against costly cyber attacks? The short answer is by selecting a security information and event management (SIEM) platform that will detect threats before they can wreak havoc. However, not all SIEMs are built to address the unique needs of SMBs, which are particularly vulnerable to the following use cases.

Phishing

Phishing is a concern for security teams across the world, and smaller organizations are as likely to be targeted as larger corporations. Look for a SIEM platform with built-in phishing detection and remediation, so SMBs know employees are protected on this vital communications channel.

Insider threats

Insider threats are another key use case, particularly with the shift to remote work. Privileged accounts, contractors and employees are everyday vectors for attackers, often via compromised credentials. When monitoring for malicious or accidental insider threats, user behavior analytics (UBA) is key to understanding the risks associated with the activity of various users in an organization.

Ransomware

Ransomware is a low-risk, low-cost, high-profitability option for attackers, so it is no surprise it's so prevalent. It is the number-one most likely threat to cause a 24-hour outage at SMBs. Out-of-the-box ransomware detection is a must, protecting an organization from paying a ransom and from the costly loss of availability.

The power of AI

One of the toughest challenges security teams face is the cybersecurity skills shortage. Organizations can take advantage of the cognitive capabilities of AI to enhance the knowledge available to their professionals — gathering and enriching context through analysis of structured and unstructured data, and reducing investigation time from hours to minutes. By separating the wheat from the chaff, analysts spend less time on low-priority incidents and more time preventing breaches or reducing their impact through timely response.

MSSPs

SMBs don't need to be alone in their fight against cybercrime; for many, the answer is a managed security services provider (MSSP) with a dedicated focus on threat detection, investigation and response. An MSSP can efficiently implement the capabilities above and mature use cases across its whole customer base while customizing as required.

Leveraging modern frameworks such as MITRE ATT&CK, SMBs and their MSSP partners can assess, implement and grow their security posture using a common language for threat actors, tactics and techniques — and benefit from threat-intelligence feeds, automation and AI tools that would be tough to deploy with limited resources. By partnering with the right MSSP, SMBs can safely focus on developing and transforming their businesses.

Offering Manager, Threat Detection & Response — IBM Security
2017 – 2018
Development Lead & Product Owner · IBM Security

Engineering lead and product owner for the QRadar Vulnerability Manager team (eight engineers).

2013 – 2016 Award
Software Engineer, then Senior · IBM Security

The QRadar platform. Built the first QRadar App SDK and the publishing path third-party developers still use — now well past half a million downloads.

◆ IBM Outstanding Technical Achievement Award · 2016

For the QRadar App Framework and SDK.

2012
Software Engineer · TradeHero, Singapore

Second engineer (fourth employee) at a fintech spin-off out of an iOS incubator, later acquired. Built the first server infrastructure and the CI pipeline.

2007 – 2012 Study
Diplôme d'Ingénieur (MSc) · INSA Rennes

A general-then-specialised engineering degree in France, with an Erasmus semester at Queen's University Belfast (2011–12), and I've been based in Belfast since.

1990
Born · Nantes, France
Tech‹